
The session addressed the risks and opportunities related to ISO/IEC 27001, Spain's National Security Framework (ENS) and the NIS2 directive. During the event, AENOR awarded Tedra the ISO/IEC 27017 cloud security certification.
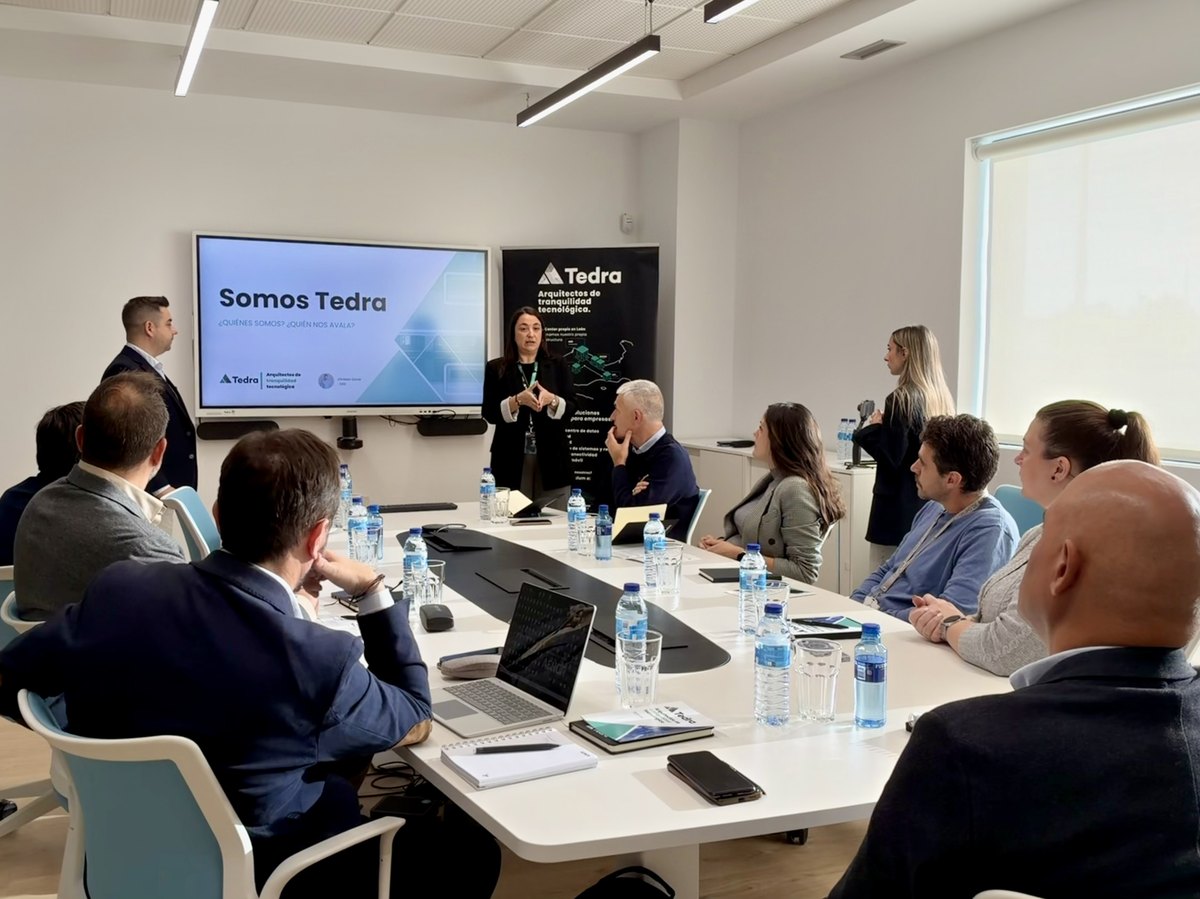
Together with AENOR, Tedra has hosted a tech coffee at its offices in León aimed at local companies and institutions to examine the main challenges posed by information security and regulatory compliance. The event made it possible to address the risks and opportunities associated with ISO/IEC 27001, Spain’s National Security Framework (ENS) and the NIS2 directive, as well as to understand how to approach their implementation from a strategic perspective.
Information security from a strategic perspective
Pencho Herrero, AENOR’s director in Castilla y León, approached information security from the perspective of certification and its role in organisations’ strategy. His talk focused on the importance of embedding security into business management and of having mechanisms in place to demonstrate compliance with applicable requirements.
For her part, Beatriz Quirós, a Compliance consultant, explained the different paths to advancing regulatory compliance, with particular attention to ISO/IEC 27001 for Information Security, the National Security Framework (ENS) and the NIS2 directive. From a business consulting perspective, her talk framed these standards as a roadmap for identifying obligations, setting priorities and guiding security efforts.
The tech coffee made it possible to share knowledge and bring the companies and institutions of León closer to the key aspects they must consider when facing the regulatory demands related to information security.
Tedra adds ISO/IEC 27017 certification to its security framework
During the session, AENOR awarded Tedra the new ISO/IEC 27017 Cloud Security certification, an international standard that sets out security controls and best practices specific to cloud services.
This certification complements Tedra’s information security framework, based on ISO/IEC 27001, by incorporating guidelines specific to cloud environments. While ISO/IEC 27001 establishes a general framework for managing information-related risks, ISO/IEC 27017 goes deeper into the particularities of security in cloud services.
Adding this certification broadens the scope of Tedra’s security framework in an area directly linked to the delivery of its technology services.